Last Updated : September 10, 2026
Changing the uninstall password for Symantec Endpoint Protection is crucial for maintaining system security. Uninstall passwords prevent unauthorized individuals from disabling or removing security software. By following a few simple steps, administrators can change their uninstall password, bolstering system defenses. Creating a strong and complex password, regularly updating it, and implementing additional security practices are essential for maintaining a secure system post-password change.
In today’s digital landscape, cybersecurity has become a paramount concern for individuals and organizations alike. One crucial aspect of safeguarding our systems is ensuring that unauthorized users cannot uninstall security software without the appropriate credentials. Together, we will delve into the importance of uninstall passwords in Symantec Endpoint Protection and provide step-by-step instructions for changing them. We will also explore best practices for creating secure uninstall passwords and address common troubleshooting issues. Moreover, we will discuss the significance of maintaining security post-password change. Let’s dive in and empower ourselves with the knowledge needed to bolster our system’s defense against potential threats.
Understanding the Importance of Uninstall Passwords
The purpose of an uninstall password in Symantec Endpoint Protection is to prevent unauthorized users from disabling or removing the security software. By setting an uninstall password, administrators ensure that only authorized individuals can make changes to the system’s security settings.
Uninstall passwords are a crucial component of a robust cybersecurity strategy, especially in corporate environments where sensitive data is at risk. They provide an added layer of defense against internal and external threats, ensuring that the security software remains intact and operational at all times.
The Role of Uninstall Passwords in Symantec Endpoint Protection
Uninstall passwords play a vital role in maintaining the integrity of Symantec Endpoint Protection. They serve as an additional layer of protection, safeguarding the software from being tampered with or deactivated without proper authorization.
Furthermore, uninstall passwords help prevent accidental or unauthorized removal of the security software, reducing the chances of system vulnerabilities and potential data breaches. By requiring a password for uninstallation, organizations can enforce strict access control measures and enhance overall security posture.
Risks Associated with Unsecured Uninstall Passwords
Leaving the uninstall password unchanged or using weak and easily guessable passwords can expose your system to potential risks. Unauthorized individuals could disable your security software, leaving your system vulnerable to malware and other malicious intrusions.
It is essential for organizations to regularly update and strengthen their uninstall passwords to mitigate the risk of unauthorized access. Implementing complex password requirements, such as a combination of letters, numbers, and special characters, can significantly enhance the security of Symantec Endpoint Protection and reduce the likelihood of security breaches.
Steps to Change Your Uninstall Password
To change the uninstall password for Symantec Endpoint Protection, follow these steps:
Ready to secure your files?
Join millions of users who trust Folder Lock to password protect their most sensitive photos, videos, and documents.
Symantec Uninstall Password
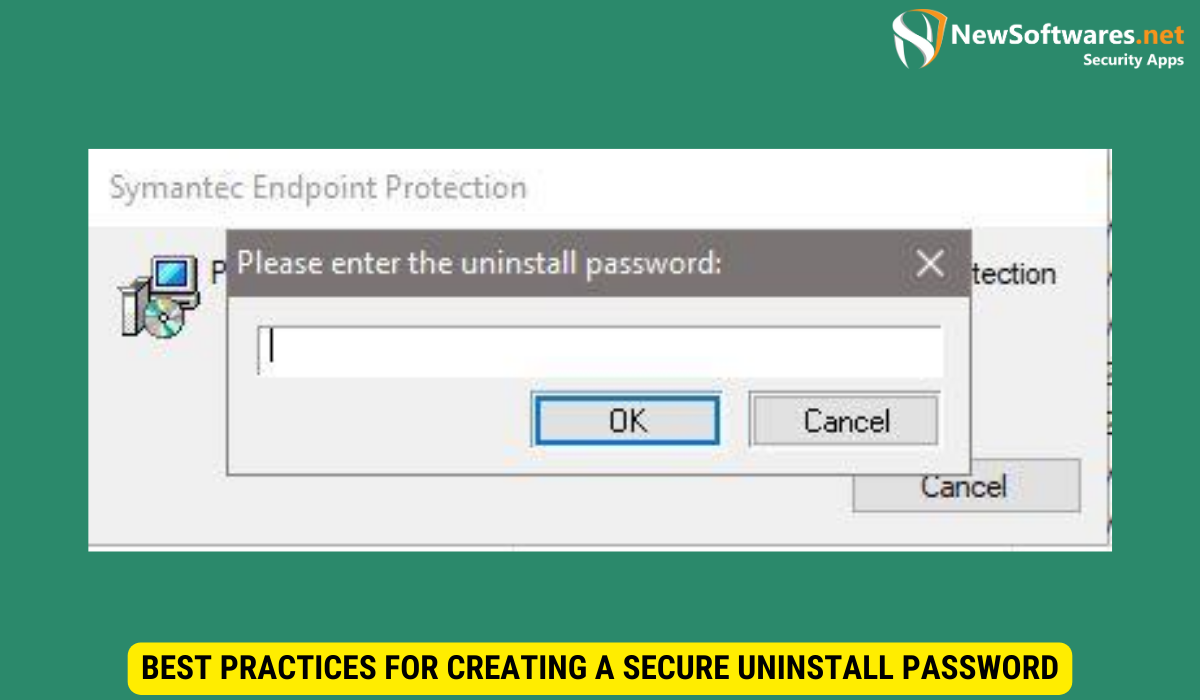
Managing your enterprise security infrastructure requires strict access controls, and the Symantec Endpoint Protection uninstall password is one of the most critical safeguards in your cybersecurity toolkit. By default, Symantec Endpoint Protection (SEP) enforces tamper protection to prevent unauthorized users, rogue applications, or sophisticated malware from disabling or removing the antivirus agent. Without knowing the designated administrative password, uninstalling the client software or altering core security configurations becomes virtually impossible, ensuring that your endpoints remain fully protected against evolving cyber threats at all times.
In many corporate environments, IT administrators overlook the importance of regularly updating or securely storing their Symantec uninstall password, leading to operational bottlenecks when migrating systems or troubleshooting software conflicts. Establishing a robust credential management policy for your endpoint security solutions prevents unauthorized tampering while allowing authorized personnel to perform necessary maintenance. Whether you are deploying software updates, upgrading to a newer version of the security suite, or transitioning to a different cybersecurity architecture, having immediate, secure access to the uninstall password is essential for seamless network administration.
Frequently Asked Questions
What is the default Symantec Endpoint Protection uninstall password?
By default, Symantec Endpoint Protection does not come with a pre-configured uninstall password. Tamper protection is usually enabled during deployment, and the password must be explicitly set and managed by your system administrator within the Symantec Endpoint Protection Manager (SEPM) console.
How can I find or reset a forgotten Symantec uninstall password?
If you have access to the Symantec Endpoint Protection Manager (SEPM), you can easily view, modify, or disable the client uninstall password under the client group’s Policy settings. If you lack SEPM access and tamper protection is locked, you may need to use advanced registry modification tools or administrative scripts authorized by your IT department.
Can I uninstall Symantec Endpoint Protection without the password?
No, if tamper protection is active and an uninstall password has been enforced, you cannot standardly remove the software through Windows Control Panel without entering the correct credentials. This security feature is specifically designed to stop unauthorized users and malware from disabling endpoint defenses.
How do I disable tamper protection to remove SEP?
You can disable tamper protection temporarily by logging into the SEPM console, navigating to the specific client group policies, and disabling the tamper protection feature. Alternatively, if you have the administrator password, you can enter it when prompted during the manual uninstallation process.